Linux ACLs Configuration Using TC-Flower
In this Document we will go through the ACLs configuration using Linux TC Flower. The flower filter is a versatile classifier that allows for detailed packet matching based on criteria such as MAC addresses, IP addresses, VLAN tags, and more.
Required Linux Modules
root@dent-1:~# lsmod
Module                  Size  Used by
act_gact               16384  0
sch_ingress            16384  0
cls_flower             53248  0
at24                   20480  0
Basic TC Flower configuration
AS shown in the following topology we have PC1, PC2 and PC3 all are in same broadcast domain.
The requirement is to block PC1 from accessing PC2.
Topology
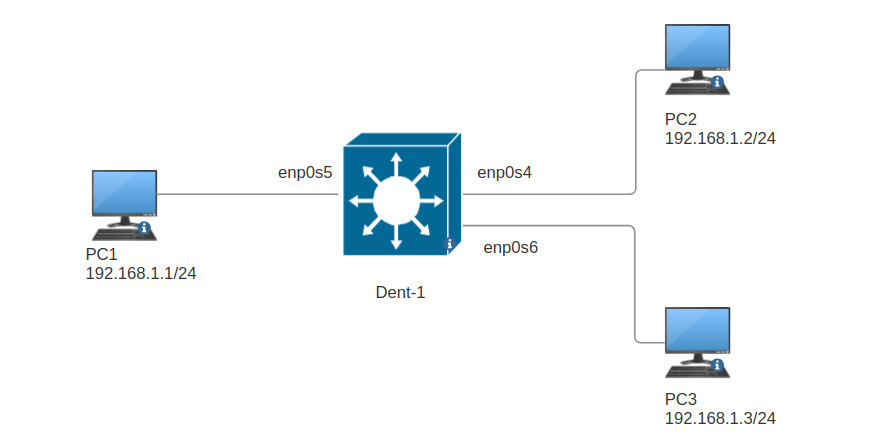
Configuration
- Create a special
Qdiscwithclsactkind. - Create
flowerfilter rule that matchPC2ip (192.168.1.2) with drop action. - Create
flowerfilter rule that allow everything else.
- ONM-CLI
- IPROUTE2
- NETCONF
qdiscs-iproute2
  special-qdisc enp0s5 clsact
tc-filters-iproute2
  dev-filter enp0s5 ingress
    rule 10
      filter flower match dst_ip 192.168.1.2/32
      filter flower actions gact drop
    rule 20
      filter flower actions gact pass
tc qdisc add dev enp0s5 clsact
tc filter add dev enp0s5 ingress pref 10 protocol ip handle 0x1 flower dst_ip 192.168.1.2/32 action drop
tc filter add dev enp0s5 ingress pref 20 protocol ip handle 0x1 flower action pass
<config>
    <tc-filters>
        <dev-filter>
            <dev>enp0s5</dev>
            <direction>ingress</direction>
            <netns>1</netns>
            <rule>
                <pref>10</pref>
                <flower>
                    <match>
                        <dst_ip>192.168.1.2/32</dst_ip>
                    </match>
                    <actions>
                        <gact>drop</gact>
                    </actions>
                </flower>
            </rule>
            <rule>
                <pref>20</pref>
                <flower>
                    <actions>
                        <gact>pass</gact>
                    </actions>
                </flower>
            </rule>
        </dev-filter>
    </tc-filters>
    <qdiscs>
        <special-qdisc>
            <dev>enp0s5</dev>
            <qdisc-kind>clsact</qdisc-kind>
            <netns>1</netns>
        </special-qdisc>
    </qdiscs>
</config>
Verify
- Now
PC1can pingPC3but noPC2
PC1> ping 192.168.1.2
PING 192.168.1.2 (192.168.1.2) 56(84) bytes of data.
--- 192.168.1.2 ping statistics ---
2 packets transmitted, 0 received, 100% packet loss, time 1001ms

PC1> ping 192.168.1.3
PING 192.168.1.3 (192.168.1.3) 56(84) bytes of data.
64 bytes from 192.168.1.3: icmp_seq=1 ttl=64 time=13.2 ms
64 bytes from 192.168.1.3: icmp_seq=2 ttl=64 time=1.49 ms